Identify Vulnerabilities.
Reduce Risk.
Protect Your Business.
RajSecure delivers independent web application penetration testing, API security assessments, cloud security audits, and offensive security consulting for SaaS companies, FinTechs, and international enterprises across the USA, UK, Germany, EU, Singapore, UAE, and India.
OUR CORE SERVICES
Professional Cybersecurity Services & Penetration Testing
We simulate real-world attacker techniques to identify exploitable weaknesses in your web applications, APIs, cloud environments, and network perimeters before malicious actors can compromise them.
Web Application Penetration Testing
Why It Matters: Eliminate exploitable vulnerabilities before attackers or enterprise customer procurement audits discover them.
Deep manual and automated offensive testing targeting authentication, session management, multi-tenant isolation, business logic flaws, and OWASP Top 10 vulnerabilities.
What We Test:
API Security Assessment
Why It Matters: Prevent unauthorized mass data exfiltration and ensure tenant data isolation across modern microservice backends.
Granular offensive evaluation of API endpoints covering OWASP API Security Top 10, broken object-level authorization (BOLA), token replay, and data leakage.
What We Test:
Cloud Security Assessment
Why It Matters: Harden cloud perimeters against credential compromise, lateral movement, and catastrophic cloud resource takeover.
Comprehensive posture, IAM privilege boundary, and attack-path assessment identifying over-privileged credentials, exposed storage, and container misconfigurations.
What We Test:
Network Penetration Testing
Why It Matters: Neutralize ransomware ingress channels, close vulnerable exposed ports, and harden edge network infrastructure.
Offensive penetration testing of external perimeters and internal network infrastructure to discover vulnerable exposed services, weak encryption, and ingress points.
What We Test:
Vulnerability Assessment & VAPT
Why It Matters: Obtain immediate visibility into publicly visible weaknesses before formal audits or customer security questionnaires.
Rapid identification and validation of external perimeter risks, exposed staging subdomains, DNS takeover vulnerabilities, and unpatched web technologies.
What We Test:
Authorized Red Team Engagements
Why It Matters: Stress-test SOC detection and response teams under controlled, real-world attack conditions to expose defense blindspots.
Scenario-driven adversary simulation testing an organization’s detection, response, and resilience capabilities against realistic multi-stage cyber attacks.
What We Test:
Mobile Application Security Testing
Why It Matters: Prevent binary reverse engineering, local data theft on compromised devices, and unauthorized bypass of in-app security controls.
Comprehensive static (SAST) and dynamic (DAST) analysis of mobile binaries, local storage encryption, runtime tampering, and backend API communication.
What We Test:
Cybersecurity Consulting & vCISO Advisory
Why It Matters: Access experienced cybersecurity leadership without the overhead of hiring a full-time Chief Information Security Officer.
On-demand senior cybersecurity consulting covering security architecture reviews, threat modeling workshops, vendor security questionnaires, and audit readiness.
What We Test:
Enterprise Security Assessments
Why It Matters: Comprehensive multi-asset validation designed to meet strict regulatory standards and satisfy institutional procurement requirements.
Tailored end-to-end security engagements combining web, API, cloud, and network testing under custom Rules of Engagement (RoE) with dedicated account management.
What We Test:
ENGAGEMENT LIFECYCLE
How Our Cybersecurity Assessments Work
We operate under strict Rules of Engagement (RoE) to ensure zero operational disruption, verifiable evidence collection, and actionable developer remediation.
We establish clear Rules of Engagement, verify written authorization, and map testing boundaries across applications, APIs, and cloud perimeters.
We analyze your architecture from an adversary perspective, identifying high-value targets, critical trust boundaries, and potential attack paths.
Our specialists execute manual and tool-assisted testing, hunting for logic flaws, authorization bypasses, and chained vulnerabilities beyond automated scanners.
We safely validate exploitable weaknesses with reproducible Proof-of-Concept (PoC) evidence, ensuring zero false positives and measuring tangible business impact.
We deliver an executive summary for leadership alongside engineer-ready technical findings with prioritized remediation code examples and hold a live debrief.
After your engineering team deploys fixes, we perform independent retesting to verify effective resolution and issue an updated report with Letter of Attestation.
Deliverables Standard
What You Receive in Every Engagement
We do not deliver automated scanner exports. Every finding is manually validated, scored using CVSS 3.1, and accompanied by reproducible Proof-of-Concept payloads and code-level remediation blueprints.
Included in Every Assessment:
- Executive Briefing for board, investors, and leadership
- Technical Vulnerability Register with CVSS 3.1 severity scores
- Step-by-step reproducible Proof of Concept (PoC) exploit evidence
- Specific developer remediation code patterns and config patches
- 1 complimentary remediation verification retest included within 30 days
- Official signed Letter of Attestation for customer audits (SOC 2, ISO 27001)
PACKAGED PROGRAMS
Productized Assessment Packages
Curated, multi-discipline security programs designed for specific technical milestones, product launches, and enterprise compliance readiness.
SaaS Security Launch
Complete pre-launch and customer-readiness security assessment for modern software platforms.
Target Profile: B2B SaaS companies, product scale-ups, and startups launching new applications or closing enterprise deals
Included in Scope:
- Web Application Security Testing
- API Security Assessment
- External Attack Surface Review
- Authentication & Authorization Deep-Dive
- Sensitive Data & Token Exposure Audit
- Remediation Verification Retest (1 included)
FinTech Security Assessment
Comprehensive multi-layer security testing safeguarding financial transactions, data, and APIs.
Target Profile: FinTech, payment gateways, banking technology, crypto platforms, and regulated financial applications
Included in Scope:
- Web Application Security Assessment
- API Security & Payment Logic Review
- Cloud Security & IAM Assessment
- Identity & Active Directory / SSO Audit
- Network & Infrastructure Security
- Business Logic & Financial Transaction Abuse Testing
- Full Remediation Verification Retest
Cloud Security Program
Holistic cloud posture, identity isolation, and attack-path review across your modern stack.
Target Profile: AWS, Azure, and GCP environments hosting microservices, containers, and data infrastructure
Included in Scope:
- Cloud Architecture & Configuration Review
- IAM Least-Privilege & Escalation Audit
- Public Asset & Storage Exposure Mapping
- Kubernetes / Container Security Review
- Cloud Attack Path Analysis
- Remediation Verification Retest
AI Security Assessment
Dedicated security testing for LLMs, RAG pipelines, AI APIs, and autonomous agent workflows.
Target Profile: AI-first startups, enterprise generative AI features, RAG knowledge bases, and AI agent deployments
Included in Scope:
- LLM Prompt Injection & Jailbreak Testing
- RAG & Vector Database Access Control Review
- AI API & Tool Execution Security Audit
- System Prompt & Model Output Data Exposure Audit
- OWASP Top 10 for LLM Applications (LLM01-LLM10)
- Prompt & Guardrail Retest Included
* Note: Displayed rates represent starting-price positions for standard scopes. Final pricing depends on scope, complexity, application size, number of endpoints, authentication roles, infrastructure, testing depth, and specific engagement requirements.
SECTOR EXPERTISE
Tailored for High-Growth Sectors
Security testing built around the specific threat models, data sensitivity, and regulatory realities of modern digital businesses.
SaaS & Technology
Multi-tenant isolation, API authentication, customer data protection, and enterprise procurement readiness.
Key Focus Risks:
FinTech & Financial Services
Transaction integrity, API security, PCI DSS compliance testing, and financial data isolation.
Key Focus Risks:
E-Commerce & Retail
Checkout security, customer account takeover prevention, inventory API protection, and fraud risk reduction.
Key Focus Risks:
Healthcare Technology
Patient portal security, medical API endpoints, telehealth platforms, and sensitive health data protection.
Key Focus Risks:
AI & Machine Learning Companies
LLM prompt injection testing, RAG vector database isolation, agentic tool execution, and model security.
Key Focus Risks:
B2B Platforms & Enterprises
Complex multi-cloud environments, adversary simulation, hybrid Active Directory, and supply chain security.
Key Focus Risks:
Serving Global Business Jurisdictions
Active International Delivery & Support
R&D AND LABS
Supporting Technology Initiatives
Our proprietary tooling and internal R&D initiatives enhance our manual penetration testing practice. These specialized software assets power our assessment methodologies across AI, forensic evidence, and personal digital defense.
RajSecure AI
Autonomous Offensive Security & LLM Assessment Architecture
Proprietary security testing suite designed to evaluate LLMs, RAG vector pipelines, and autonomous agent workflows against prompt injection, data exfiltration, jailbreaks, and unauthorized tool execution.
RajSecure EPR
Evidence Protection & Incident Response Platform
Tamper-proof digital evidence preservation and orchestrated incident response framework engineered for enterprise security operations confronting security incidents, internal breaches, or legal disclosure.
RajSecure Shield
Personal Digital Safety Firewall
Prevention-first Android personal digital safety firewall engineered to eliminate digital leverage, personal coercion, and blackmail vectors before threats escalate into catastrophic extortion.
Note: RajSecure is primarily a cybersecurity services and consulting firm. Our technology projects serve as proprietary R&D frameworks that support our client engagements.
LEADERSHIP & TECHNICAL OVERSIGHT
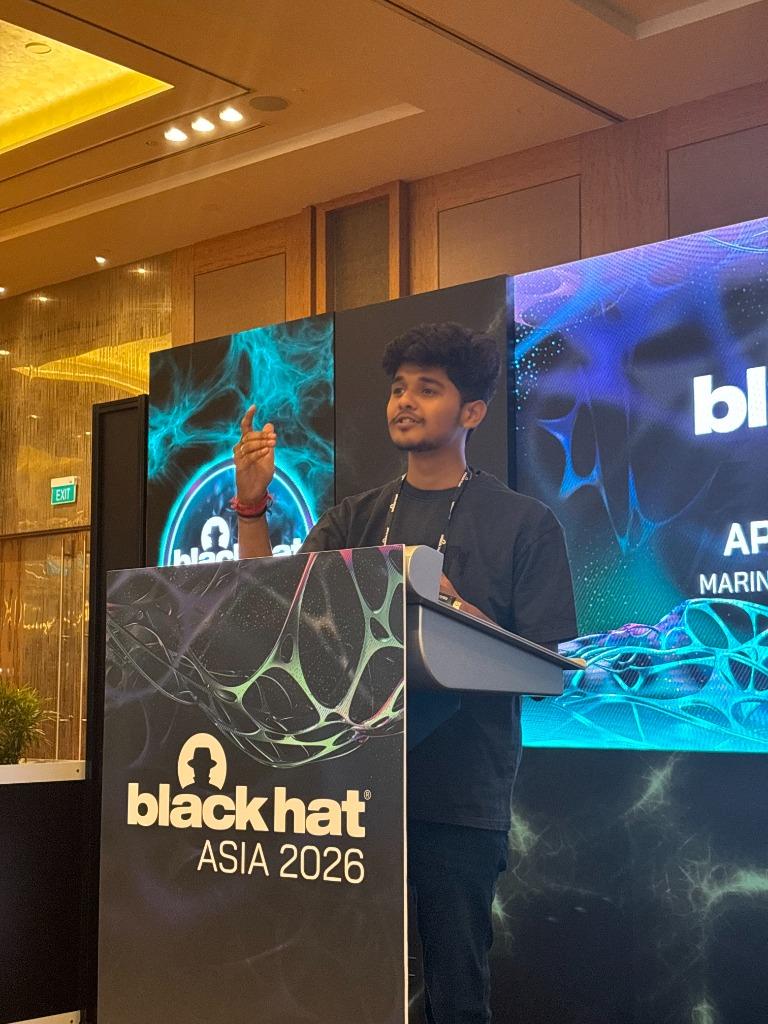
Raj Kumar
Founder & CEO, RajSecure
“Every cybersecurity assessment we conduct is rooted in technical truth. We don't sell automated scan summaries dressed up as reports. We dig into authentication boundaries, analyze nuanced business logic, and deliver verified exploit chains that protect our clients from real-world adversaries.”
Raj Kumar directs RajSecure’s offensive security research, red-team methodologies, and client delivery. Drawing from active engagement with international cybersecurity research communities like Black Hat, he maintains hands-on technical oversight on all client deliverables.
FREQUENTLY ASKED QUESTIONS
Engaging With RajSecure
Clear answers regarding authorization requirements, assessment scopes, deliverables, international billing, and confidentiality.
How does an engagement start with RajSecure?
An engagement starts with an initial discovery call or scoping form submission where we define your objectives, target assets, and timeline. We then provide a formal proposal with defined Rules of Engagement (RoE). Testing begins only after mutual execution of a Non-Disclosure Agreement (NDA) and written authorization.
Do you require written authorization before testing?
Yes, absolutely. RajSecure strictly adheres to ethical security practices and requires documented, written authorization confirming that your organization owns or has explicit legal rights to authorize testing on all specified target systems.
How long does a typical security assessment take?
Most standard web application or API assessments take between 5 to 10 business days to execute, followed by report preparation and debrief. Complex environments, multi-asset scopes, or red team simulations typically take 2 to 4 weeks depending on agreed milestones.
Do you support authenticated (grey-box) testing?
Yes. In fact, authenticated (grey-box) testing is highly recommended for web applications, APIs, and cloud environments. It allows our security team to evaluate role-based access controls, multi-tenant boundaries, and privilege escalation vulnerabilities between different user tiers.
What does the final security report contain?
Our deliverables include an Executive Summary outlining business risk and posture for leadership, a detailed Technical Findings section with CVSS 3.1 ratings, step-by-step reproducible Proof of Concept (PoC) evidence, business impact analysis, and practical remediation guidance with code/config examples.
Do you provide remediation guidance and developer support?
Yes. We provide actionable, developer-friendly remediation steps for every finding. Additionally, we conduct a technical debrief call with your engineering and security teams to answer questions and assist in clarifying effective mitigation strategies.
Do you provide retesting after we patch vulnerabilities?
Yes. Most of our assessment packages include complimentary remediation verification within 30 to 45 days. Once your team deploys patches, we re-test the specific findings to verify effective resolution and issue an updated final report and Letter of Attestation.
Can RajSecure sign our mutual Non-Disclosure Agreement (NDA)?
Yes. We routinely execute bilateral NDAs with our international B2B clients before discussing sensitive architecture details, scoping documentation, or testing credentials.
GET STARTED TODAY
Identify Vulnerabilities. Reduce Risk.
Protect Your Business.
Whether preparing for enterprise customer audits, releasing a new API, or verifying cloud defenses, RajSecure delivers authorized, evidence-backed security testing.